Run it · 15 of 19
Protocols
JMAP and SMTP are required; IMAP, POP3 and ManageSieve are optional, and each can be switched off on its own, per tenant or server-wide.
On this page
inbuxa speaks JMAP, IMAP, POP3, SMTP, ManageSieve, CalDAV, CardDAV and WebDAV. Two of those are required. The rest are supported in full, and optional.
What is required
| Protocol | Why it cannot be switched off |
|---|---|
| SMTP | It is how mail arrives and leaves. Port 25 has to answer the internet. |
| JMAP | It is how the console and the webmail talk to the server. |
What is optional
| Protocol | Port | Permission |
|---|---|---|
| IMAP | 993 | imapAuthenticate |
| POP3 | 995 | pop3Authenticate |
| ManageSieve | 4190 | sieveAuthenticate |
Each of these is a permission, not just a port. That distinction is the whole point: closing a port stops connections reaching the server, while removing the permission means the server will not authenticate that protocol for those people even if something reaches it.
Ports
Settings › Network › Listeners (ports) opens with the standard ports as one table: each port, what it's for, its encryption, and whether it's open, with a switch.
| Port | For |
|---|---|
| 25 | Receiving mail from other servers |
| 587, 465 | Sending from mail apps |
| 443 | Webmail, the console, JMAP apps, automatic setup |
| 80 | Redirect to HTTPS, and HTTP certificate checks |
| 993, 143 | Reading mail in IMAP apps |
| 995, 110 | Downloading mail with POP3 |
| 4190 | Editing filters from mail apps (ManageSieve) |
IMAP, POP3 and ManageSieve, and the sending ports while legacy mail is off, are switched on the Security page, so their rows link there. Other listeners you made are listed under the table, and in full below it.
Open here means the server listens. Whether the internet can reach it also depends on your firewall and hosting provider, which is what Reachable from outside, under the table, checks:
- In a cluster, each server tries the others' ports every 10 minutes, over the internet, by their public names, as a sender would. For each port and server it shows who got through, and who didn't and why ("no answer within 5 seconds"). A port counts as reached only when every address its name resolves to answers, so a firewall rule missing for IPv6 shows up. Only a connection is made; nothing is sent.
- On a single server, it can't: a connection to its own public address
never leaves the machine, so it would pass whatever the firewall in front
blocks. It says so, lists whether each port is listening, and leaves the
outside check to you, from another network:
nc -vz <the server's name> <port>.
Switching one off
IMAP, POP3 and ManageSieve each have their own switch, so you can stop POP3 and keep IMAP. One more action turns them all off at once, with sending from mail apps, so that only the webmail and JMAP apps can sign in. All of it works for the whole server or for one tenant.
For the whole server
In the console, Settings › Security › Security, Legacy mail protocols, under the security to-do list. Each protocol has a row with its ports, how many accounts used it in the last 30 days, and what it does now. IMAP, POP3 and ManageSieve each have a switch on their row.
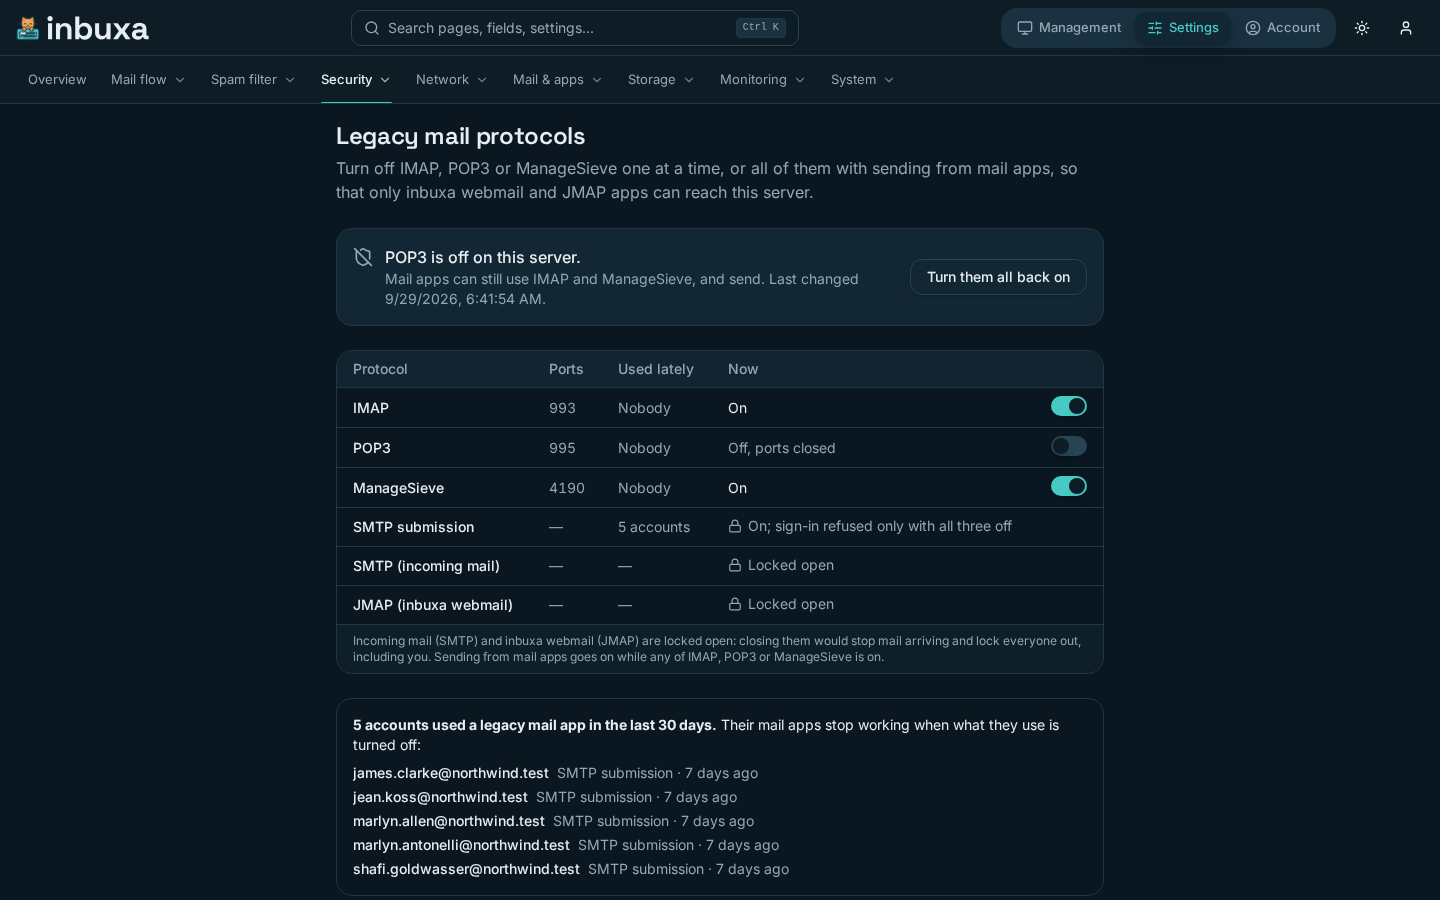
Turning one off asks first. It names the accounts that used that protocol in the last 30 days and the ports that close. Its listeners close, so those ports stop answering, and sign-in over it is refused. The other protocols, sending from mail apps and the webmail carry on.
Turn off all legacy protocols… turns all three off at once. It first
lists every account that used a mail app in the last 30 days, and says what
stays working: incoming mail, calendars and contacts, and the webmail, which
can be installed as an app. To confirm, type turn off legacy mail. With
all three off:
- IMAP, POP3 and ManageSieve listeners close.
- Sending from mail apps (SMTP submission) stops working, but its ports stay open: mail apps are told they can't sign in.
Sending from mail apps is refused only while all three are off. Turning off one or two never stops mail apps sending. Incoming mail (SMTP) and the webmail (JMAP) are locked open whatever you do, because closing them would stop mail arriving and lock everyone out, including you.
Autoconfig, autodiscover and the suggested DNS records stop offering whatever is off, one protocol at a time.
While all three are off, the console's dashboard shows a Legacy off chip. People see a notice in the webmail's security settings, naming what's off when only some protocols are. Turning a protocol back on is one click and reopens its listeners; Turn them all back on does it for all three. If a port has been taken by something else meanwhile, the page lists the listeners it couldn't reopen, with Try again.
Your firewall is still yours
The switch stops inbuxa answering on those ports. Firewall rules, port forwards, a load balancer or proxy that still send them to the server are yours to change.
For one tenant
The same switches, for one organization, on the tenant's page in the console. The tenant's own administrator can use them; they need no one else's leave. Legacy mail apps on the tenant in the webmail's Administration turns all three off or on at once, and says which are off when only some are.
For a tenant, the ports stay open, because other tenants share them. Instead, sign-in over what's off is refused for the tenant's domains and accounts, which stops password guessing and stolen-password logins against them. Other tenants are unaffected. An organization that has finished with POP3 can stop answering it without you standing up a second server for the ones that haven't.
The server's switch wins
A protocol off for the whole server is off for every tenant. While it is, a tenant can't turn that protocol back on for itself, and is told which one. Sending from mail apps stops for a tenant when the server's and the tenant's switches together leave all three off.
Deciding
Turning IMAP and POP3 off is not automatically the right call. They are how every desktop and mobile mail client that is not the webmail connects, and turning them off strands those people.
Reasonable reasons to do it:
- An organization has standardized on the webmail, and IMAP is only a way in for credential stuffing.
- POP3 in particular is rarely wanted, and it downloads and deletes by default, which is a data-loss shape nobody asks for on purpose.
- ManageSieve is only needed by people editing filters from an external client; the webmail edits them over JMAP.
Reasonable reasons not to:
- Anyone using Thunderbird, Apple Mail, Outlook or a phone's built-in mail app.
- Anything automated that reads a mailbox.
What this is not
This does not turn off filters. Sieve scripts still run on the server as mail arrives whether or not ManageSieve is reachable — ManageSieve is only the protocol for editing them from outside the webmail.
It also does not affect CalDAV, CardDAV or WebDAV, which ride the same HTTP listener as JMAP and have no separate authentication permission of their own.